What’s Vulnerable › Vulnerabilities
CVE-2020-23754
- Severity: critical (CVSS 9.6 v3.1)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 1.6% probability of exploitation in the next 30 days
- Public exploit or detection template: none known
- Published: 2021-11-02 · updated 2026-06-17
- Weakness: CWE-79
Description
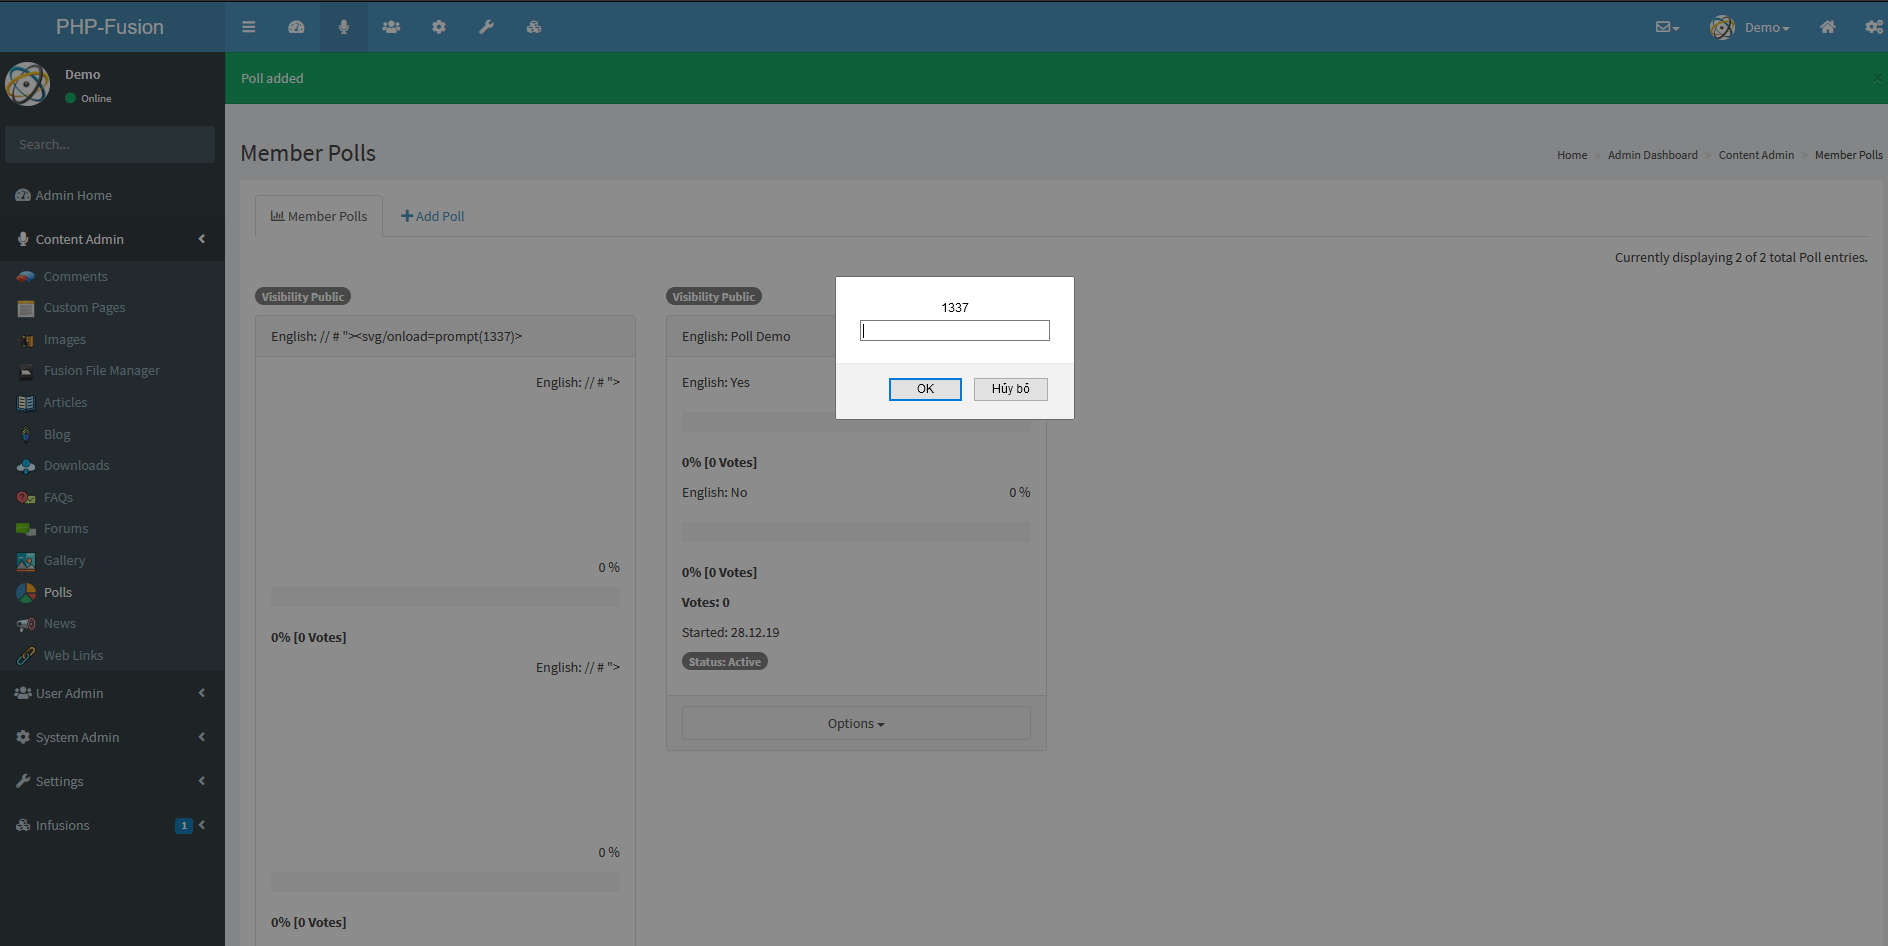
Cross Site Scripting (XSS) vulnerability in infusions/member_poll_panel/poll_admin.php in PHP-Fusion 9.03.50, allows attackers to execute arbitrary code, via the polls feature.
Affected products
- PHPFusion: 9.03.50
References
- https://github.com/php-fusion/PHP-Fusion/issues/2315
- https://user-images.githubusercontent.com/62001260/81574006-6fb70480-93cf-11ea-814c-55a96d2fe95e.PNG
- https://user-images.githubusercontent.com/62001260/81574112-9412e100-93cf-11ea-9493-615a70162034.PNG
- https://github.com/php-fusion/PHP-Fusion/issues/2315
- https://user-images.githubusercontent.com/62001260/81574006-6fb70480-93cf-11ea-814c-55a96d2fe95e.PNG
- https://user-images.githubusercontent.com/62001260/81574112-9412e100-93cf-11ea-9493-615a70162034.PNG

Get alerted when CVE-2020-23754 or the next vulnerability affects your stack