What’s Vulnerable › Vulnerabilities
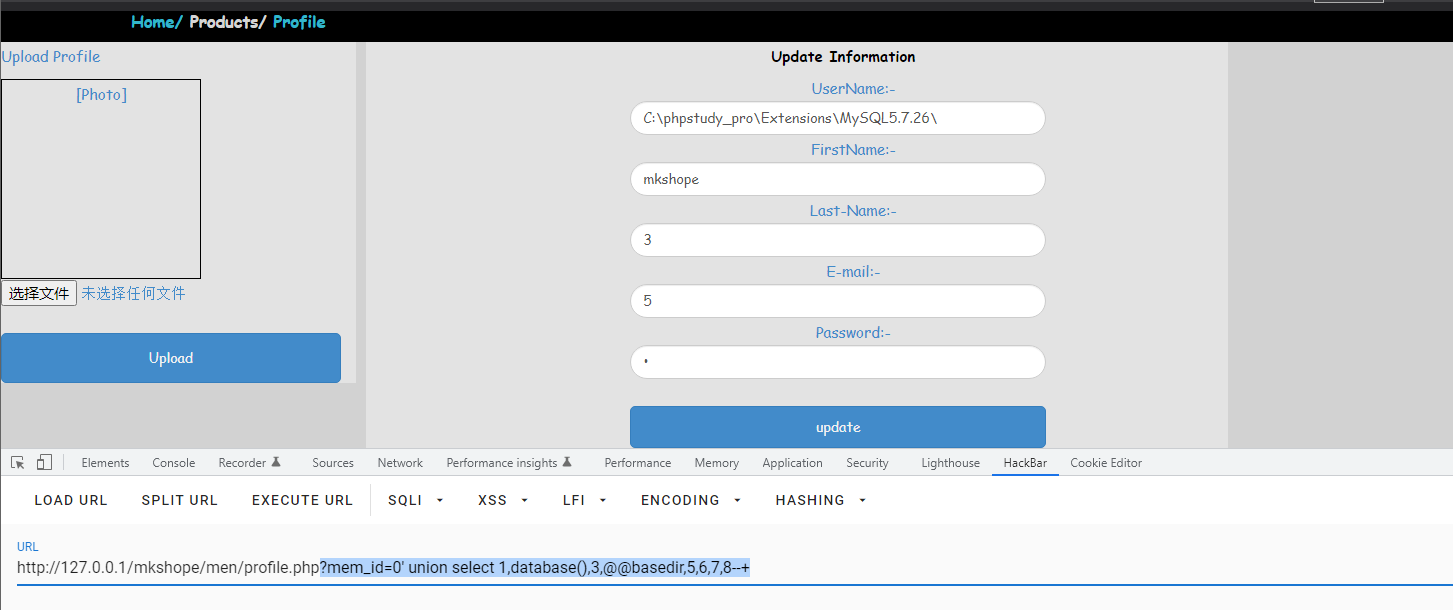
CVE-2022-2957: SourceCodester Simple and Nice Shopping Cart Script profile.php sql injection
- Severity: critical (CVSS 9.8 v3.1)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 0.9% probability of exploitation in the next 30 days
- Public exploit or detection template: yes
- Published: 2022-08-25 · updated 2026-06-17
- Weakness: CWE-89
Description
A vulnerability classified as critical was found in SourceCodester Simple and Nice Shopping Cart Script. Affected by this vulnerability is an unknown functionality of the file /mkshop/Men/profile.php. The manipulation of the argument mem_id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The identifier VDB-207001 was assigned to this vulnerability.
Affected products
- SourceCodester Simple and Nice Shopping Cart Script: all versions
References
- https://s1.ax1x.com/2022/08/14/vUSruD.png
- https://vuldb.com/?id.207001
- https://s1.ax1x.com/2022/08/14/vUSruD.png
- https://vuldb.com/?id.207001
Get alerted when CVE-2022-2957 or the next vulnerability affects your stack