What’s Vulnerable › Vulnerabilities
CVE-2026-8254: Devs Palace ERP Online sales_save cross site scripting
- Severity: low (CVSS 2.4 v3.1)
- Exploited in the wild: not listed in CISA KEV
- EPSS: 0.3% probability of exploitation in the next 30 days
- Public exploit or detection template: none known
- Published: 2026-05-11 · updated 2026-07-24
- Weakness: CWE-79
Description
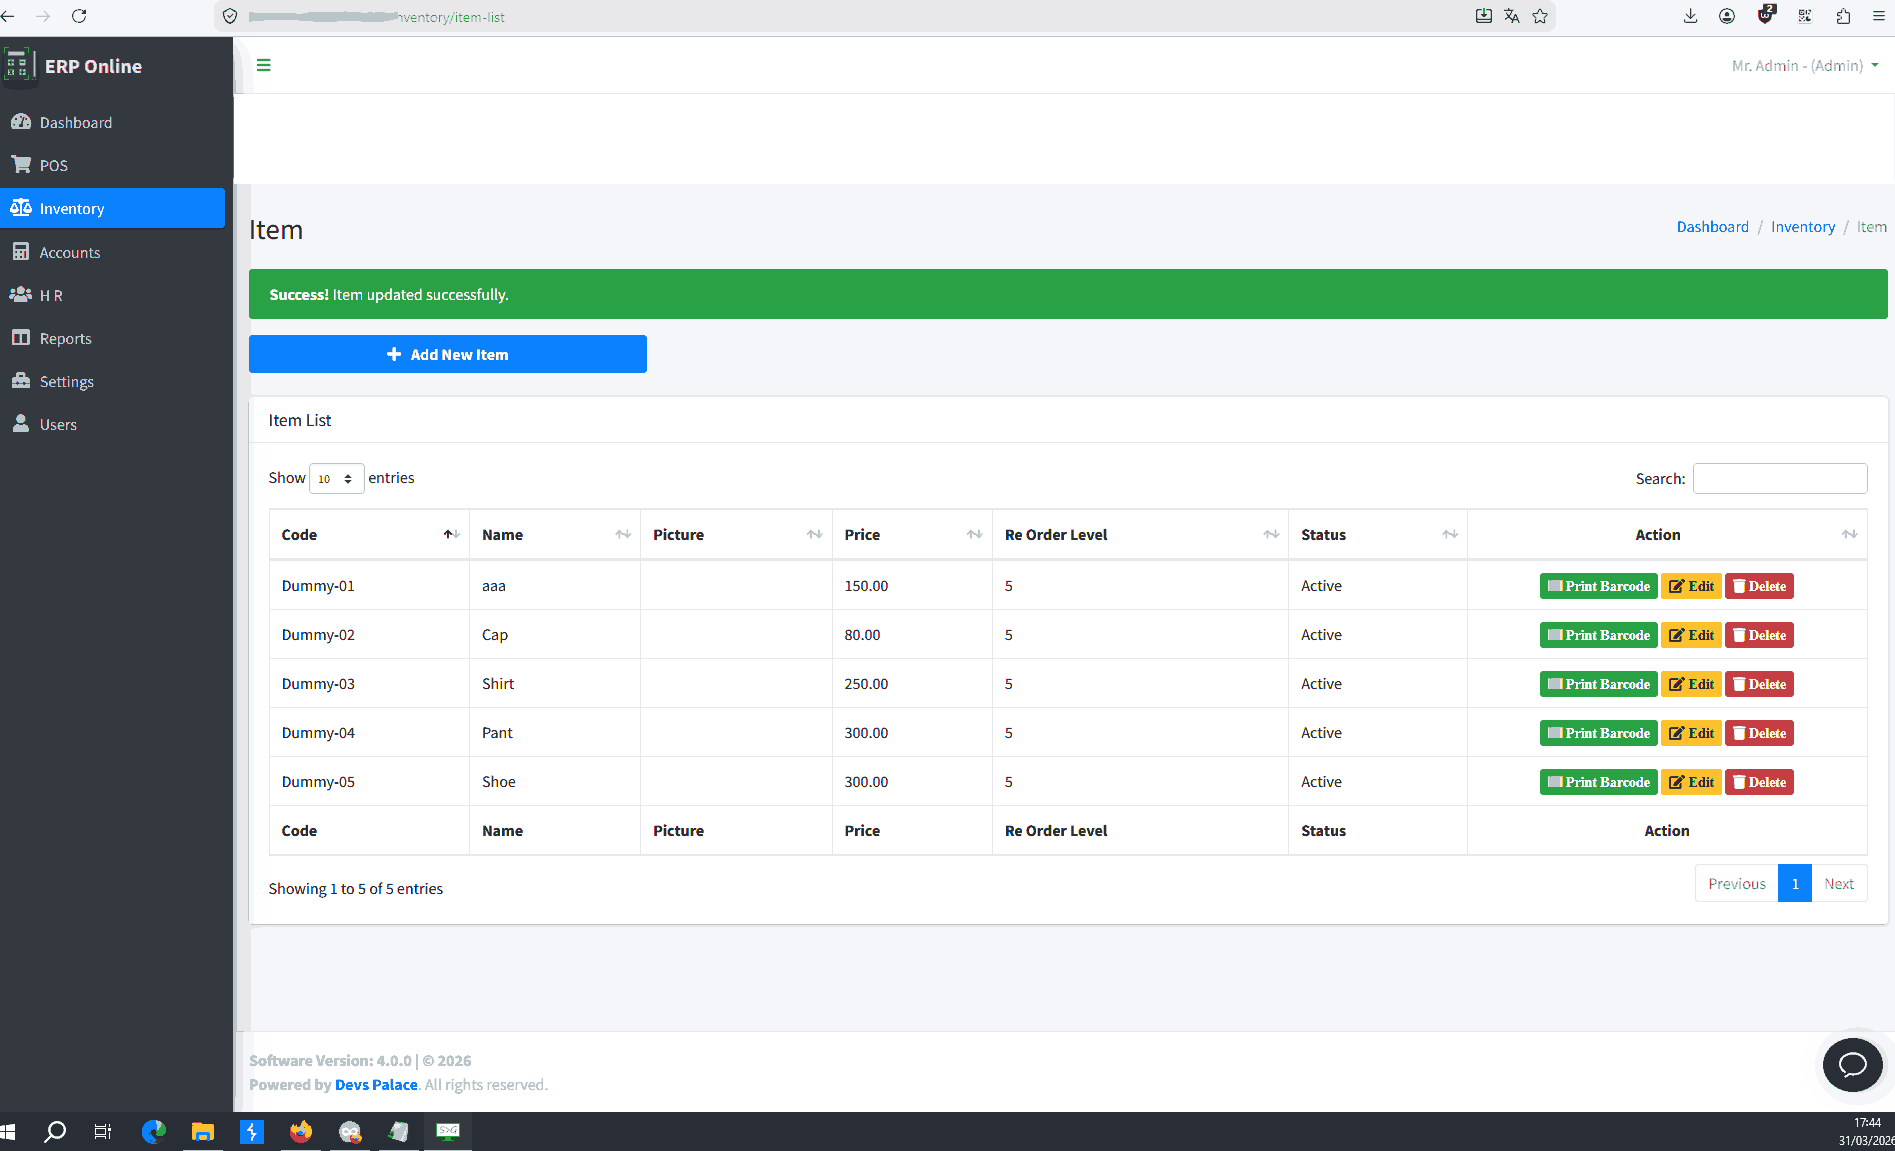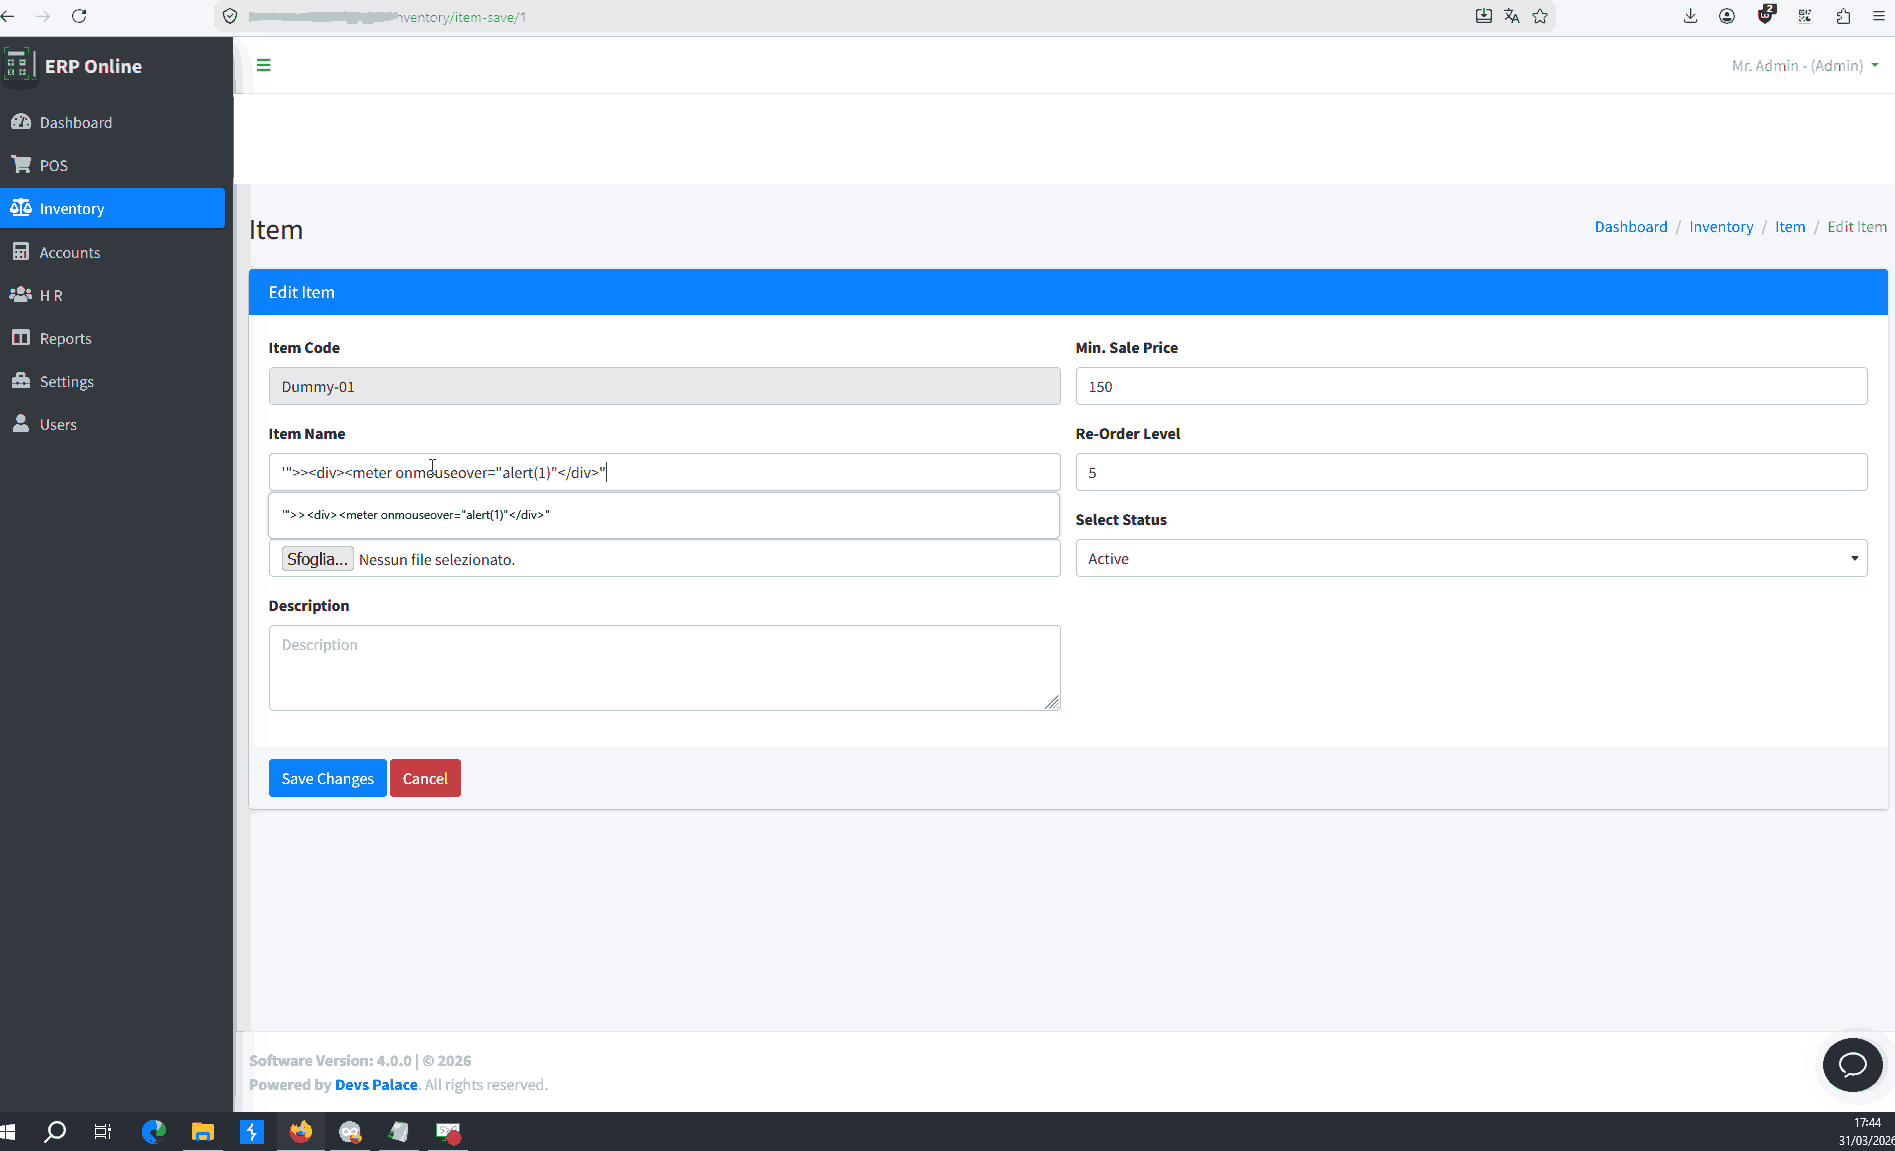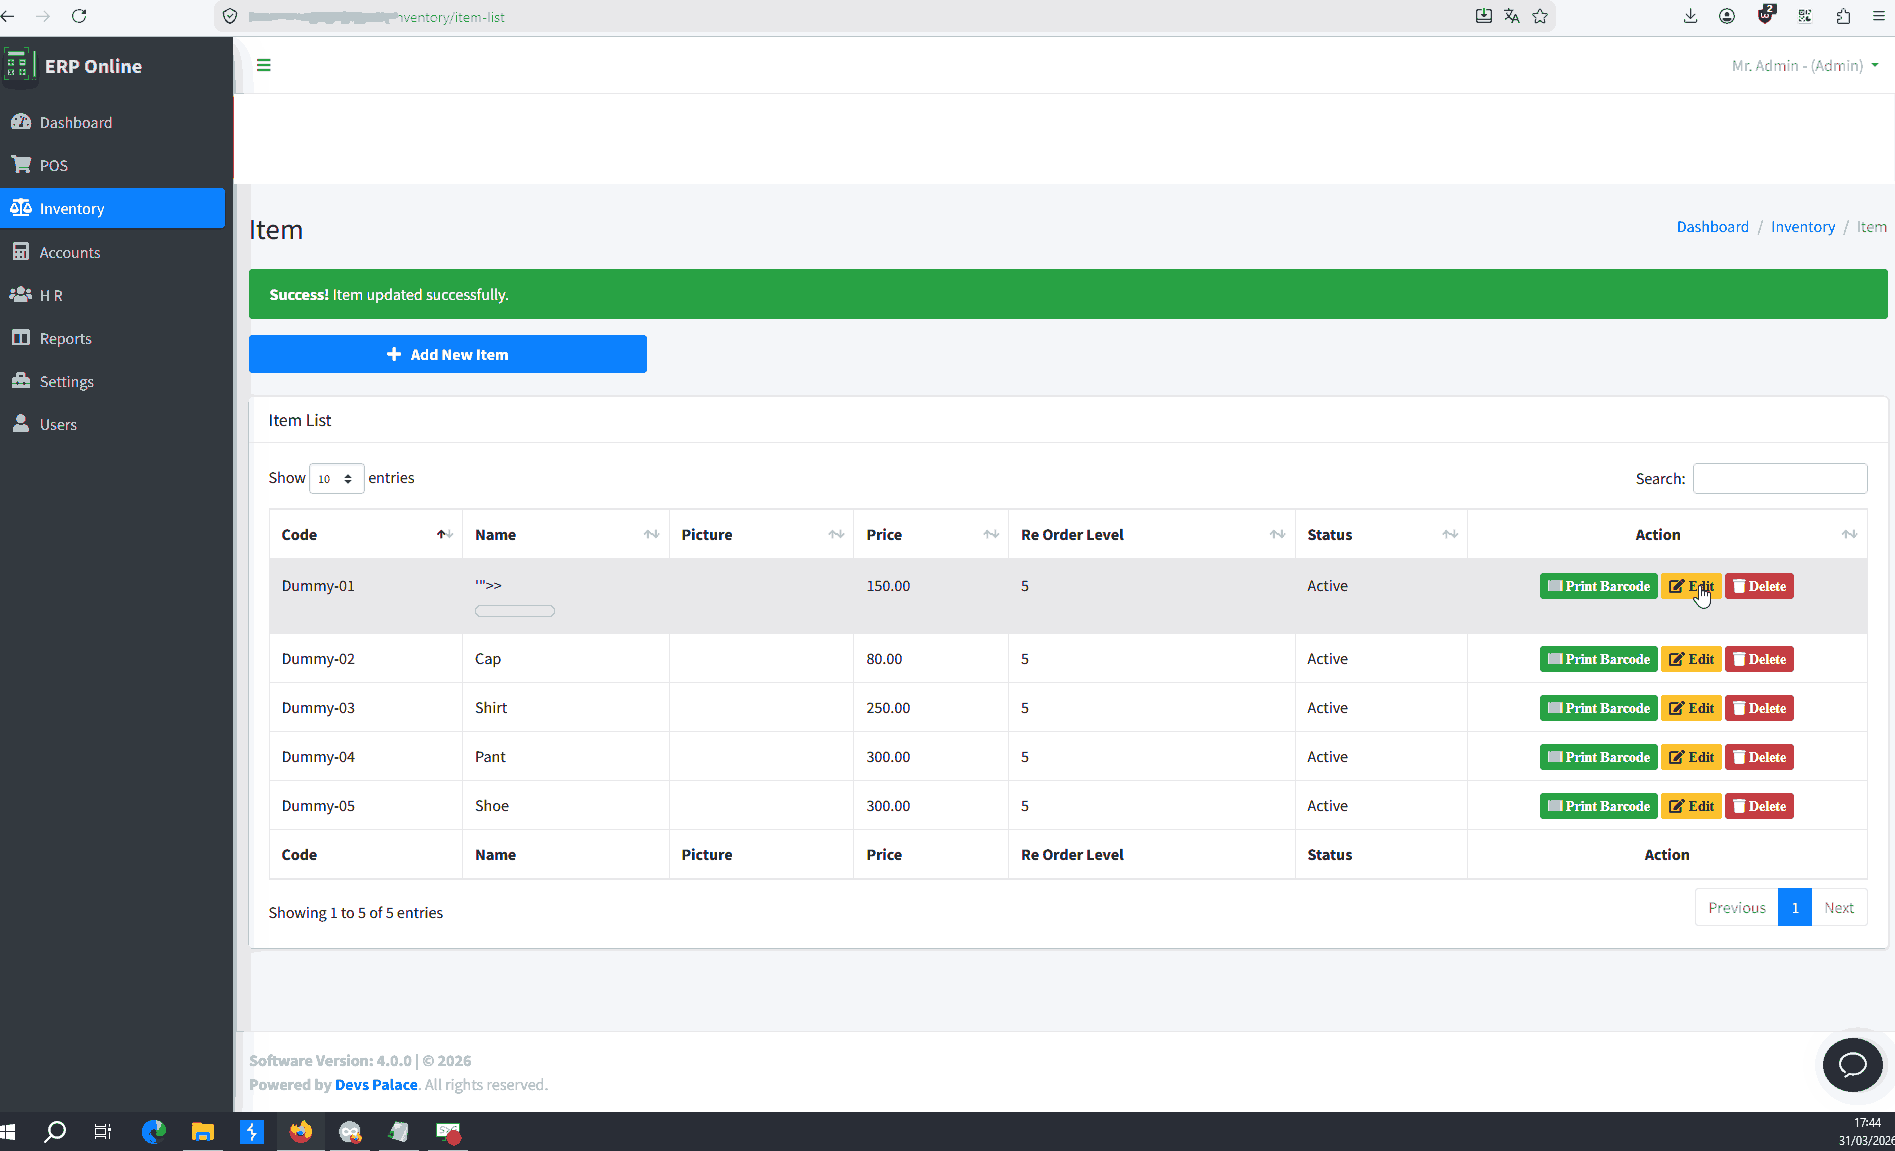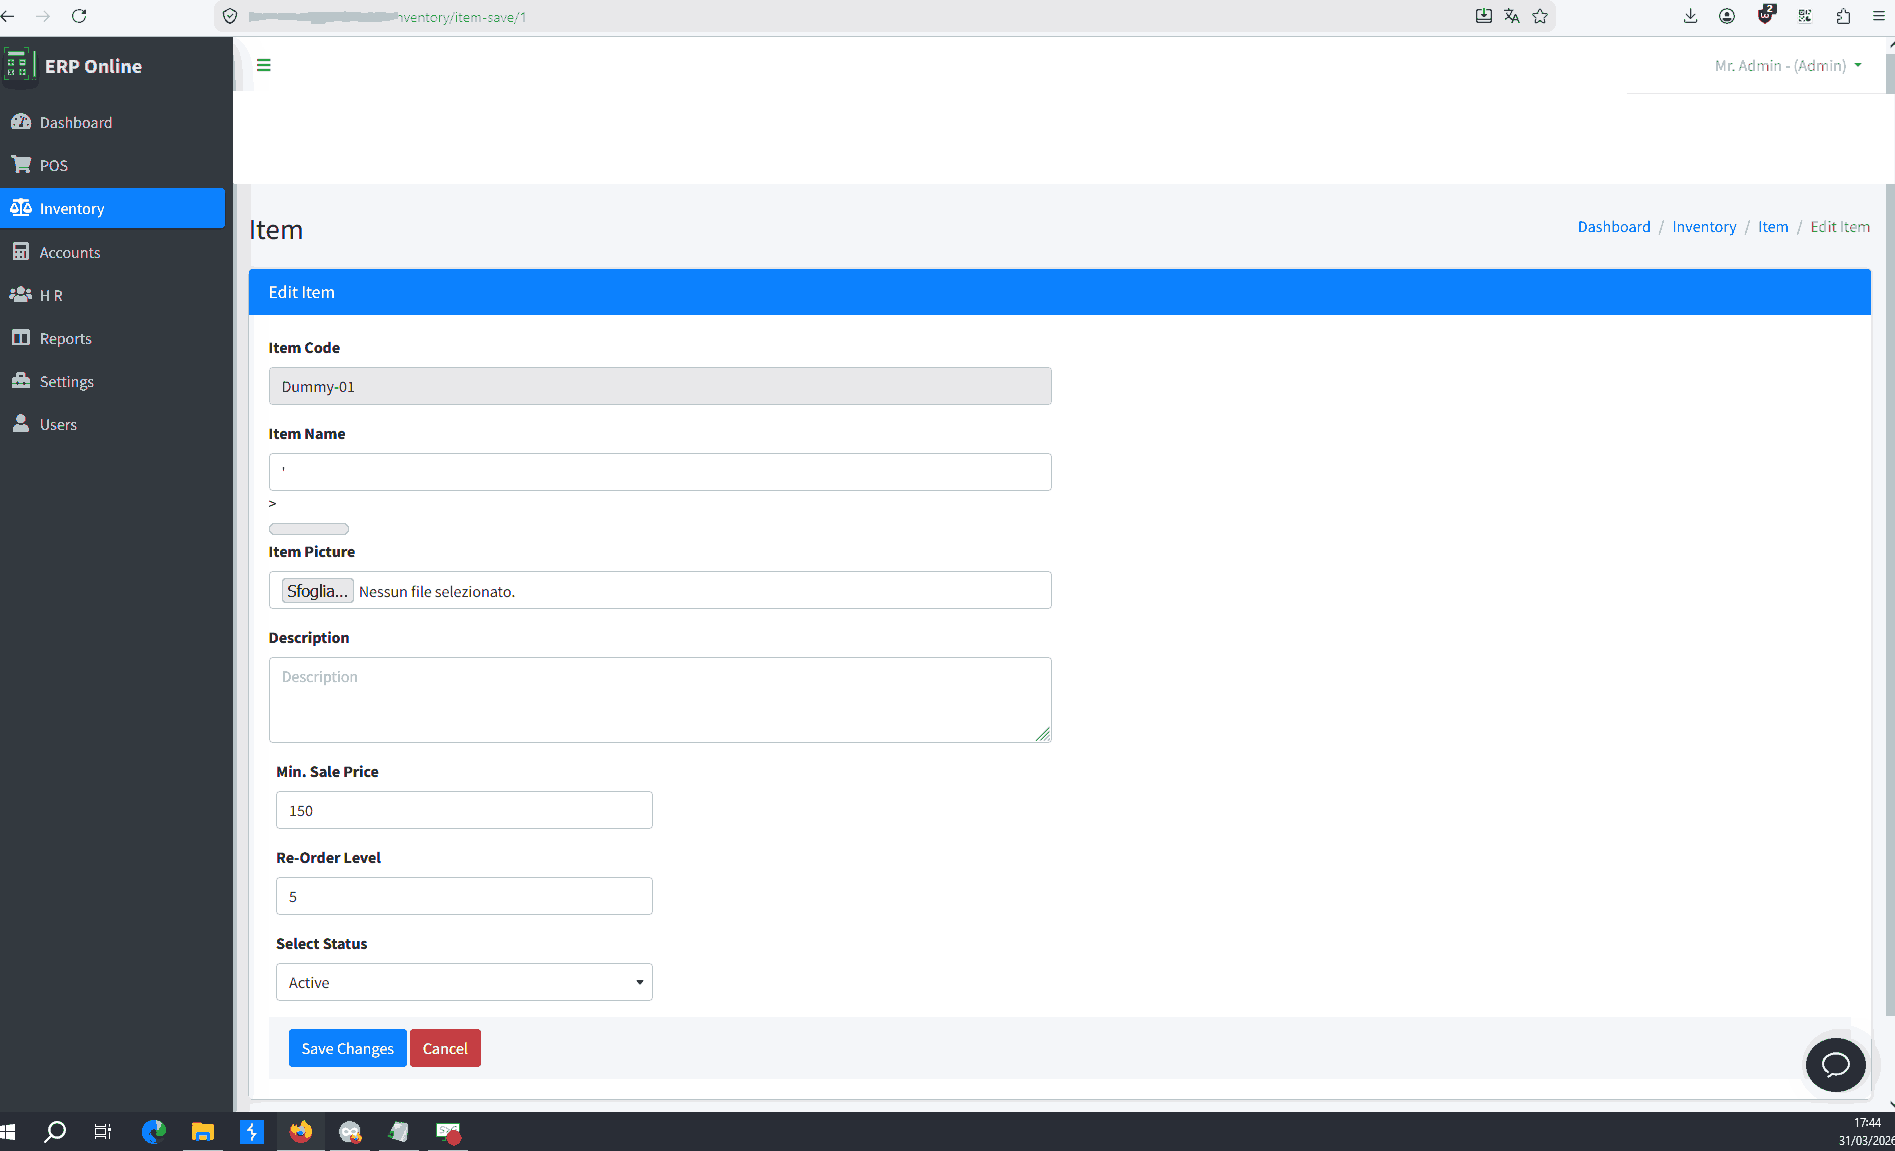
A security flaw has been discovered in Devs Palace ERP Online up to 4.0.0. Affected by this issue is some unknown functionality of the file /inventory/sales_save. The manipulation results in cross site scripting. It is possible to launch the attack remotely. The exploit has been released to the public and may be used for attacks. The vendor was contacted early about this disclosure but did not respond in any way.
Affected products
References
- https://olografix.org/acme/_poc/ERP_Online-POC1.gif
- https://vuldb.com/submit/808279
- https://vuldb.com/vuln/362551
- https://vuldb.com/vuln/362551/cti
Get alerted when CVE-2026-8254 or the next vulnerability affects your stack